The Shadowserver Foundation is an all volunteer watchdog group of security professionals that gather, track, and report on malware, botnet activity, and electronic fraud.
Their recent Bot numbers here.
Sunday, January 07, 2007


Early Warning Bark Worse Than Bite

An Israeli firm has designed a security system to ensure jailbreakers or intruders find a guard dog's bark can indeed be worse than its bite.Harnessing technology that interprets barking -- to see if an animal is responding to a threat instead of just routinely woofing -- the company aims to replace or supplement expensive electronic surveillance systems.
"There is currently very little utilisation of the watchdog's early warning capabilities," says privately owned manufacturer Bio-Sense Technologies, based in the Israeli town of Petah Tikva,on its Web site.
Friday, January 05, 2007
Life and Death? Medical Identity Theft
Business Week has an article about the risk of “medical identity theft”.
When Lind Weaver opened her mailbox one day in early 2004, she was surprised to find a bill from a local hospital for the amputation of her right foot. Surprised because the 57-year-old owner of a horse farm in Palm Coast, Fla., had never had worse than an ingrown toenail.
WikiLeaks
WikiLeaks good or bad thing?
WikiLeaks is developing an uncensorable version of WikiPedia for untraceable mass document leaking and analysis. Our primary targets are highly oppressive regimes in China, Russia, central eurasia, the middle east and sub-saharan Africa, but we also expect to be of assistance to those in the west who wish to reveal unethical behavior in their own governments and corporations.
Friday Fun - Police hold camel over murdering a buffalo!
 The camel got it in the end anyway... Full story here.
Abdul Waris Ali Shah, a resident of the area, had tied up his camel he had bought for Rs 38,000 for sacrifice. Sometime later, another resident of the same area Gulfam tied his sacrificial buffalo near the camel.
In the night, the camel fell upon the buffalo, bit the latter in the chest and gave it numerous blows with its front legs and killed it.
The other day when Gulfam, reached the spot to pick up his buffalo, he found it dead and rushed to the nearby police station to lodge an FIR against Abdul Waris.
And, interestingly, the police took the camel into custody, apparently for murdering the fellow mammal!!
Thursday, January 04, 2007
Domaintools.com
Like other sites like DNSstuff.com, etc. Domaintools.com offers some handy online tools - many are for free. One of the things I like about Domaintools is that you can subscribe to an alert service that will let you know when a new domain with certain keywords has been registered. This can be a helpful tool for identifying Phishing sites before the emails start to fly...
Check them out here.
Wednesday, January 03, 2007
Computer Hacker Steals $150,000 from Portage County Clerk of Courts Office
Read between the lines and I don't think this was a "hack" at all but just an old fashion case of fraud. This whole story seems a tad ignorant...
"With computers today you don't have to be anywhere close to the scene to commit some serious thefts..The ability to bank electronically is a major convenience to us but a huge security risk," said Stevens Point Police Chief Jeff Morris.
Chief advises that if you have an on line bank account check it daily. Also beware of people asking for your PIN, Social Security number or other information over the Internet.
Tuesday, January 02, 2007
Detecting temperature through clock skew
Steven Murdoch's presentation about how people can unmask an anonymous online publisher by remotely monitoring his computer's temperature.
Even if that computer moves location and changes ISP, it can be later identified through this clock skew. In addition to varying between computers, clock skew also changes depending on temperature. Thus a remote attacker, monitoring timestamps, can make an estimate of a computers environment, which has wide-scale implications on security and privacy.
Monday, January 01, 2007
Secure Future - Toddler Found Playing Along Busy Highway
 Hopefully this scary event is the key to a safe and secure new year for this innocent boy and his sister...
(12-31) 12:22 PST Indianapolis (AP) --
Drivers swerved cars and trucks into other lanes to avoid a 3-year-old boy, wearing only a diaper and T-shirt, who was playing along a busy highway after wandering away from home while his mother slept, police said.
Some motorists stopped along Interstate 465 on the city's west side Saturday to take care of the boy until officers arrived, the Indiana State Police said.
Police said they traced the toddler to an apartment at a nearby complex, where they found his mother, Nancy Dyer asleep in a filthy apartment and his 2-year-old sister eating spaghetti off the floor.
Child Protective Services took the boy and his sister into custody, and investigators said the agency also had been called to the apartment Thursday because the boy was outside unsupervised.
Sunday, December 31, 2006
Spy Numbers Stations on Shortwave Radio
Grandma give you a shortwave radio for Christmas? Have some fun with it here.
"59372 98324 19043 78903 95320...". The mechanized female voice drones on and on... What have you stumbled on to? Instructions to spies? Messages exchanged between drug dealers? Deliberate attempts at deception and mis-information?
Chances are, all of the above! What you've tuned in to is called a "Spy Numbers Station". They've been on the air for several decades, and only recently have the mysteries started to unfold. But there's still much we don't know about these mysterious stations. With the information on these pages, you'll discover the little that we do know about these stations, what we're still trying to learn, and how you too can tune in to the spies.

Let's Hope for a Happy New Year...

In a span of a few hours, 2,973 people were killed in the Sept. 11, 2001, terrorist attacks. In a span of 45 months, the number of American troops killed in Iraq has exceeded that grim toll...
"An eye for an eye makes the whole world blind."
- Mahatma Gandhi
Friday, December 29, 2006
Daddy get you a new car for x-mas? Lockpicking - BMW decoder tool
Here is a video showing the demonstration of a BMW lock decoder tool and software that allows you to open almost any BMW lock.
You are going to put your Call Center where?
Indian banks, government and commercial sites have seen a very large increase in defacements and phishing attacks in 2006 according the the CERT-In.
Analysis of defaced Indian websites year-2006 (till June) (ciwp-2006-02)
Analysis of defaced Indian websites year-2006 (till June) (ciwp-2006-02)
Wednesday, December 27, 2006
CISSP, CISA, and SSCP Open Study GROUP Online Quizzer
An updated version of a handy online quizzer engine for CISSP, CISA, SSCP, HIPAA, and SOX.
More info here.
More info here.
Tuesday, December 26, 2006
On the Tuesday before Christmas...
my mom accidentally gave to me - An MP3 player full of pornography.
On Tuesday, Chanell Martin gave her 12-year-old daughter an early Christmas present as a reward for helping out weekends at the family's Lincoln Mall store.
Her daughter, a sixth-grader, was delighted with the black Microsoft Zune media player Martin purchased earlier that day at the Evergreen Park Wal-Mart.
But not for long.
Martin went to her room while her daughter plugged the device, which can play music and video, into the family's computer.
"She said, 'Mom -- what's this?' " Martin said. "When she handed (the player) to me she was looking at a gay orgy."
On the Zune's hard drive, Martin discovered, was about 6-- hours of hardcore gay pornography and a "slideshow" of another 62 pornographic images.
Full story here.
Sunday, December 24, 2006
Secure Air Space - Track Santa
 For more than 50 years, NORAD and its predecessor, the Continental Air Defense Command (CONAD) have tracked Santa.
NORAD Santa tracker here.
Saturday, December 23, 2006
Tis The Season - Christmas.exe
 Tis that time of the year when the malware writers out there are going to send their holiday cheer packed in an seasonally named file. This time it's Christmas.exe...
There is a good article about it over on f-secure. Check it out here.
New Year - New Look
Figured it was time for a new look... Let me know what you think...
Happy Holidays!
Happy Holidays!
Friday, December 22, 2006
Friday Fun - Tour XM
 Some Washington Post's folks took a tour of DC-based XM Satellite Radio's New York Avenue complex. At blog.washingtonpost.com...
Tuesday, December 19, 2006
The Silver Bullet Security Podcast
In the ninth episode of The Silver Bullet Podcast, has Gary McGraw interviewing Bruce Schneier. In this episode, they discuss the connection between physical security its technological component, the idea of risk management, the intersection of economics and security, and the ideas of “wholesale surveillance” and “security theater.” They also discuss patch Tuesday, hack Wednesday, and Microsoft’s approach to software security...
XSS Intro/Demo
XSS stands for cross site scripting (CSS) Since CSS is already taken by Cascaded Style Sheets, it is named XSS X standing for a Cross. It is a kind of hacking which allows you to deface websites, loggin as another user etc.
More info here.
More info here.
Friday, December 15, 2006
Sunday, December 10, 2006
Question of the day
Things that make you go hmmm...
"Wonder if any of the Allbrittons (Joe, Robert, Barbie) will be going to Chile for the funeral of Augusto Pinochet???"
Getting Hacked Results In Armed Police Raid
A Denver woman who didn't have adequate security on her home computer paid the price.Serry Winkler was visited by several officers with a search warrant who demanded that she turn over her computer.They were investigating a case of computer fraud. The woman's computer was apparently infected by a bot or robot.
Watch video.
Full story here.
Watch video.
Full story here.
Thursday, December 07, 2006
Guardian comments on ".bank"
The Guardian newspaper has a story about why do museums have a secure, restricted .museum top-level domain but banks don't have .bank?
You would think that banks get phished via fake domains much more than museums do...
"There are no safeguards whatsoever against someone registering a domain name and using it for nefarious purposes," says Richard Martin, a business security consultant at the UK clearing bank group Apacs. Barnaby Davis, director of electronic banking for Barclays, says: "We're well past the tipping point when something needs to be done that makes it harder to register URLs or makes the consequences for misuse harsher."
Full story here.
Wednesday, December 06, 2006
The Cheapskate’s Infosecurity Toolbox
From CSOonline.com
A list of free-to-download tools for the budget-pinched CISO
A list of free-to-download tools for the budget-pinched CISO
BartPE: Preinstalled Environment
Troubled by that incessant spyware or virus that just doesn't seem to go away? Need a way to troubleshoot a system without booting the operating system installed on it? BartPE and the right plug-ins will let you do this. www.nu2.nu/pebuilder
Snort: Open Source Intrusion Detection System
Arguably the world's most used Intrusion Detection System. Both Windows and Linux binaries are available. www.snort.org
VMWare Server: A virtual environment
It finally happened: VMWare is available for free. Patch management, QA, vulnerability remediation testing and other daily activities are now available without a significant capital investment. VMWare also offers images of various environments, configurations and operating systems available for download (they're called "appliances") and ready to use in conjunction with the main product. Just download, point VMWare to the image and test away! www.vmware.com/products/server
DataRescue's IDA Pro Freeware 4.3 disassembler and debugger
Although not posted on the DataRescue site anymore, the free version of their utility will turn up with a quick Google dig. Try www.programmersheaven.com/
OllyDbg disassembler and debugger
Probably the world's most used debugger disassembler. Gives most commercial debuggers a good run for their money. www.ollydbg.de
eEye Digital Security's Binary Diffing Suite
A good, free suite of binary diffing tools you can use to see the effect that a released patch may have on your environment. Read the website, as there are some platform dependencies. research.eeye.com/html/tools/RT20060801-1.html
Cygwin: Linux-like environment for Windows
Need to run some scripts or programs that previously ran only under Linux? Do you miss your Linux command line when running Windows? www.cygwin.com
Nagios: An open-source host, service and network monitoring program
Not for security only, but Nagios can be used to monitor for events that typically have security implications. This is one that you and your CIO will agree upon. www.nagios.org
iptables and Firewall Builder: Firewall and Management Interface
Don't have the deep pockets for a Checkpoint, Cisco or Juniper? Iptables comes with most Linux distributions. Not comfortable using a command line to manage it? Firewall Builder is an intuitive way to install and manage the rule set. Get a couple of credit card CDs, create a bootable distribution, and you've got a firewall in your pocket. www.iptables.org and www.fwbuilder.org
Apache SpamAssassin: Fight Spam at the Gateway
Not really a secret to most people. With the right configuration this is difficult to beat no matter how much you spend on an antispam solution. spamassassin.apache.org/index.html
OpenSSH for Windows: Secure Shell for Windows
Because FTP is so passé (and insecure), use OpenSSH on the server side coupled with "PuTTY" and WinSCP on the client side for a cheap way to secure your file transfers. sshwindows.sourceforge.net, www.chiark.greenend.org.uk/~sgtatham/putty and winscp.net
Cheops-ng: "The Network Swiss Army Knife"
A tool for mapping and monitoring your network. This is an excellent free way to track down most of the systems on your network. cheops-ng.sourceforge.net/download.php
ACID (Analysis Console for Intrusion Databases):
An analysis engine to search and process security events generated by various intrusion detection systems, firewalls and network monitoring tools. acidlab.sourceforge.net
Body of missing CNET editor James Kim has been located
The saddest part of this story is that if Mr. Kim would of stayed with his car and family, he would sill be here. Certainly his heart was in the right place, but almost every survival expert will tell you - to say with your car especially in the winter, cold and snow...
Kim, 35, left his family's stranded car Saturday morning searching for help and never returned. Kim apparently traveled in an 8-mile circle and was found less than a mile, separated by a sheer cliff, from where his family's station wagon got stuck in the snow. Officers said there was no way to determine whether he was trying to return to his starting point or if he became disoriented.
"He was very motivated...he traveled a long way," Josephine County Undersheriff Brian Anderson said.
Related Links:
http://jamesandkati.com
Mom, 2 kids survive
A commercial satellite-imagery company said Tuesday it is rerouting one of its satellites to fly over the Oregon wilderness where rescue crews search for CNET editor James Kim.
How To Survive If Lost In Wilderness - CBS News
Firewall for RFIDs
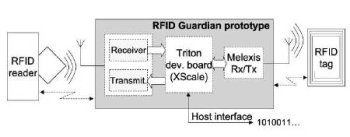 A Platform for RFID Security and Privacy Administration - This paper is a must-read paper for anyone who cares about electronic privacy and who wants to catch a glimpse of the future...
ShmooCon '07 Tickets On Sale Now!
The Early Bird tickets for December are already sold out! If you want $75 tickets, ck back on Jan 1st.
To register for ShmooCon, click here.
Important Dates and Deadlines:
To register for ShmooCon, click here.
Important Dates and Deadlines:
- December 1, 2006 - first round of ticket sales
- January 1, 2006 - second round of ticket sales
- February 1, 2007 - last round of ticket sales
- Early Bird Tickets - $75, Overall Qty to be sold - 300
- Open Registration - $150, Overall Qty to be sold - 450
- I love ShmooCon Tickets - $300, Overall Qty to be sold 50
Monday, December 04, 2006
Christmas Themed Hacker Challenge
Ed Skoudis's Christmas Themed Hacker Challenge...
"Hey, challenge fans! To close out the year, I've posted a Christmas-themed hacker challenge, this one based on the movie, A Christmas Story. You remember that one... with the Messy Marvin kid, the interesting lamp, and the Red Rider Beebee gun. In this challenge, you get to help Ralphie explore his Old Man's network, trying to retrieve a copy of his parent's Christmas gift list. But, be careful, or else you'll hack your eye out! Entries are due by December 22, when we'll award three winners a copy of my book."
Sunday, December 03, 2006
Criminals find way to disable internet
Very interesting post detailing how criminals are hijacking portions of the internet and thousands of sites. The internet hijackers are re-directing sites to one-page spam sites where they collect ad revenue by people clicking on the ads. Sometimes the internet hijackers are just doing it for minutes at a time, other times for hours.
Saturday, December 02, 2006
Machines of Loving Grace
It always amazes me that this was written in 1963...
All Watched Over by Machines of Loving Grace,
by Richard Brautigan (1963)
I like to think
(and the sooner the better!)
of a cybernetic meadow
where mammals and computers
live together in mutually
programming harmony
like pure water
touching clear sky.
I like to think
(right now, please!)
of a cybernetic forest
filled with pines and electronics
where deer stroll peacefully
past computers
as if they were flowers
with spinning blossoms
I like to think
(it has to be!)
of a cybernetic ecology
where we are free of our labors
and joined back to nature
returned to our mammal
brothers and sisters
and all watched over
by machines of loving grace.
Wednesday, November 29, 2006
psiphon to be released December 1st 2006
psiphon is a human rights software project developed by the Citizen Lab that allows citizens in uncensored countries to provide unfettered access to the Net through their home computers to friends and family members who live behind firewalls of states that censor.
Read about and download it HERE
Read about and download it HERE
A Couple of Free Password Generators
http://password.10try.com/
or
http://www.winguides.com/security/password.php
or
http://www.winguides.com/security/password.php
Friday, November 24, 2006
$3 Pen-Sized Digital Camera
How can you go wrong for $3 bucks? Stocking Stuffer here I come!
Check out the DigiCam's specs:
- Sensor Type: CIF/CMOS
- Interface Type: USB
- Resolution: 640x480 VGA
- Video: 9 fps hi-res, 20 fps low-res
- Memory: 2Mb – 20 to 80 images
- Dimension: 4.9" x 1.2" x 0.8"
- Batteries: AAA x 2 Alkaline Batteries
- Battery Capacity: Continuous Snapshots for 2 hours
- Stand-by can work about 2 weeks
- USB Power: When connected the camera draws its power from PC
- Viewable Angle: 54 degrees
Thursday, November 23, 2006
Holidays are for Kids...
How easy is it to pick a lock you ask? Most locks you come in contact every day are so easy even a 9 year old child can pick a lock their first time if you show them how!
Watch this short video! 9 Year Old Lock Picker
Monday, November 20, 2006
'Worm' attacks Second Life world
Virtual world Second Life had to close its doors for a short time on Sunday after a worm attack called grey goo.
The self-replicating worm planted spinning gold rings around the virtual world, which is inhabited by more than a million users.
Players treated the attack with a mixture of mirth and anger.
"Can this game get any more unpredictable and exciting?" asked one user, Loretta Lurra on the official Second Life blog.
As users interacted with the rings they replicated, resulting in a slowdown on the servers used by Second Life's creators Linden Lab, in California.
Second Life has become one of the most talked about developments in cyberspace in recent years.
Panty Raid
Portland Officer in Panties Case Admits, Resigns
ELIZABETH SUHThe Oregonian (Portland, Oregon)
A Portland police officer pleaded guilty Monday to two counts of official misconduct for asking two women to show him their underwear during a traffic stop in July.
In a plea bargain, John Alexander Wood, 31, agreed to resign, have his police certification revoked immediately and face two years of probation and 100 hours of community service.
Portland Police Chief Rosie Sizer said in a news conference that she was disturbed to learn of the allegations and praised the complaint and review system that acted swiftly to investigate.
The two women reported the incident to police July 26, five days after it happened. Police encouraged the women to file a complaint with the Independent Police Review Division. After the women did so, detectives began a separate investigation and Wood was placed on paid administrative leave. Wood was hired as a Portland police officer in January 2003 and was working as a district patrol officer at the time of the incident.
In the course of investigation, detectives contacted a third woman who also said that Wood asked her repeatedly to show him a tattoo on her groin.
"Community members should be able to trust sworn police officers," Sizer said. "It is my hope that the community will view this as the isolated case it was."
The Oregonian is not naming the two victims.
In a hearing Monday afternoon before Multnomah County Circuit Judge Jean Kerr Maurer, one of the women, who is from Spokane and in her early 20s, spoke of how the traffic stop plagues her every day.
"I have trouble sleeping, and I am still unable to drive at night alone," the woman said, reading from a prepared statement. "Every time I see a law enforcement official, I feel as though I can't breathe and I start to feel nauseous."
Wood wrote letters of apology to the two women, who read them after the hearing, said their attorney, John Allison.
The women told detectives they had spoken with Wood as they were leaving Dukes, a nightclub in East Portland, in the early morning hours of July 21, according to interview records released by police. Wood was in the parking lot in a marked patrol car.
The women claim Wood pulled them over while they were driving home on Interstate 205 at about 3:15 a.m. and told them to lift their skirts and show him their underwear or he would take them to jail for driving under the influence. The women said that Wood also asked them if they had breast implants and if they shaved their pubic hair.
The women said they complied with Wood's requests and he concluded the stop without writing a ticket.
Wood initially denied all allegations in interviews with detectives, saying he had contact with the three women but had not made inappropriate demands.
Allison, the attorney, said Wood couldn't be charged with sexual assault because he didn't touch the women. But, Allison said, Wood made a "full and complete admission" of his crimes in his letter to the women.
In the second incident, which occurred shortly after the first, a woman said Wood approached her and her boyfriend while they were parked in a van outside Ventura Park at Southeast 113th and Pine streets, according to police interviews.
She said she showed Wood a tattoo on her groin three times after he asked to see it under threat she would go to jail for failing to have proper identification on her. The woman is now in custody at the Multnomah County Detention Center for an unrelated probation violation.
Wood is the second law enforcement officer to come under scrutiny recently for inappropriate demands during traffic stops.
A criminal investigation begun in November 2004 found that Multnomah County Sheriff's Deputy Christopher Green asked several women he stopped to either lift their shirt up, remove their bra or unzip their pants while pretending he was searching for a suspect with a flower tattoo. The inquiry also showed Green lied about what he did when questioned by a supervisor.
Green remains on paid leave as the Oregon Department of Public Safety, Standards and Training board considers revoking his police certification. The Multnomah County district attorney's office also has renewed a criminal inquiry into Green's actions.
Game Consoles - High Risk?
Gartner: Crims will use PS3 to crack crypto
That's the opinion of Gartner's Steve Prentice, voiced yesterday at the firm's ITxpo/Symposium in Sydney.
Prentice said PlayStation 3 will pack an impressive 207 teraflops of power under its slim hood when released locally next year. By comparison, his research indicates that the .entry level. machine from supercomputer Cray offers 230 teraflops.
"There will be millions of PlayStation 3's sold, and they will all be online," he said, predicting that the sheer computing power available between the machines will be among the largest and most powerful computers ever assembled.
That power, he believes, will attract criminals.
Sunday, November 19, 2006
Hole-in-wall thief used MP3 player
 A UK thief outwitted sophisticated banking security systems by using an ordinary MP3 music player to bug cash machines and steal customers’ credit card secrets.
Maxwell Parsons, 41, was the central figure in a gang who went on to steal goods worth hundreds of thousands of pounds in high street stores across Britain.
The banking industry was so alarmed by the gang’s method, believed to be unique in this country, that they immediately moved to plug the technological loophole.
Parsons, a well-known criminal figure, was jailed for 32 months after pleading guilty at Minshull Street Crown Court to deception and unlawful interception of a public telecommunications transmission.
The fraudster learnt how to carry out the fraud from the example set by criminal gangs in Malaysia where the method of fraud was used with devastating effect against the banking system.
Parsons or other gang members would use MP3 portable music players to record data transmitted from free-standing ATM cash machines. The data was then converted to readable numbers using a separate computer programme.
Friday, November 17, 2006
Friday Fun - Reflecto-porn
Instances Reflecto-porn have been growing on sites such as eBay. The idea is that you photograph something whilst wearing your birthday suit and ensure that an image of your nether regions appears reflected in a mirror or the product - e.g. a kettle - that you’re trying to sell.
Examples and more info here.
Examples and more info here.
Sunday, November 12, 2006
Medusa Parallel Network Login Auditor
Medusa is intended to be a speedy, massively parallel, modular, login brute-forcer. The goal is to support as many services which allow remote authentication as possible.
More info and download here.
More info and download here.
Friday, November 10, 2006
Skill Crane from ShmooCon Lives!
 At last year's ShmooCon they had the Hacker Arcade with a skill crane that was hooked up to a PC and available to control over the local wireless network and the Internet. Someone ended up winning most of the skill crane prizes by writing an automated script to hit every spot. I won a Shmoo ball from the dang thing (the old fashion manual way) and now its back online.
Cypherpunks: Its A Word
The Oxford English Dictionary has added cypherpunk. Along with bling, Disneyfied and hard-ass.
Tuesday, October 31, 2006
Info Sec Search Site - 100 Resources and Counting
After some more research and digging, www.searchinfosec.com now presents results from over 100 quality security resources, from a single search box.
Sunday, October 29, 2006
Boarding Pass for one Bin Laden/Osama
A computer security student says terrorists would have no trouble getting around the government’s no-fly list, and to prove it he set up a Web site (it’s down now) that prints fake boarding passes.
The passenger name on the fake boarding pass is “Bin Laden/Osama,” although travelers can put in their own name — or a fake one — and change the flight information, too.
Christopher Soghoian, a 24-year-old doctoral student at Indiana University, said he set up the site to prove that the Transportation Security Administration isn’t taking airline security seriously.
Soghoian said terrorists on the no-fly list could use a fake boarding pass to avoid the no-fly list because IDs are only checked when the passenger passes through TSA screening. So someone could use a fake boarding pass with an ID that matches and get through the screening.
Soghoian said he built his Web site to mimic Northwest Airlines boarding passes because he had one handy after flying Northwest earlier this week. He said he has nothing against the airline.
Soghoian said the fake boarding pass couldn’t get anyone onto a flight — as long as the airline’s computers were working — because the bar code wouldn’t match the other information on the pass.
At his blog he relates the tale of FBI visits following publication of his jest and his current status.
Monday, October 23, 2006
Q&A: Why Metasploit Publishes Hacker Tools
H.D. Moore, Metasploit founder, developer, and researcher talks about why it's important to publish security exploits, his organization's relationship to the cops, and more.
Certification Top 10 Lists Revisited
This is from CertMag.com and is getting a good bit of coverage. Go and see where your certs fit and plan you next few.
Here's the winners:
Best Hands-On Programs: Certified Professional Information Technology Consultant (CPITC)
Best Supporting Materials: (ISC)2 Certified Information Systems Security Professional (CISSP)
Best Specialty Certifications: Brocade Certified SAN Designer (BCSD)
Toughest Recertification Requirements: Cisco Certifications
Best Vendor-Neutral Credentials: Building Industry Consulting Services International (BiCSi)
Most Technically Advanced Programs: (ISC)2 Certified Information Systems Security Professional (CISSP)
Best New Programs or Certs: (ISC)2 Associate Program
Best Entry-Level Certifications: Certified Wireless Network Administrator (CWNA)
Tuesday, October 17, 2006
MySpace Predator Caught by Code
Five months ago, Wired News senior editor and former hacker Kevin Poulsen whipped up 1,000 lines of computer code that scoured MySpace’s 1 million plus profiles for 385,932 registered sex offenders in 46 states.
Kevin did a praiseworthy job. His detailed article at Wired is here.
Monday, October 16, 2006
Ophcrack LiveCD v.1.1.3 released
A new version of the LiveCD with the latest version of ophcrack 2.3.3 as well as bkhive2.
List of Podcasts with a 'Security" Focus
Name: PaulDotCom Security Weekly
Main Subject: anything related to computer security
Format: Casual
Approx. Updates Per Month: 4 to 5
Recent Subjects Covered: mobile malware, hacking ATM machines, tool that allows for hosts to communicate over wireless without being associated, Spamhaus in trouble, Filtering IM for kids, Hacking Web 2.0 Applications with Firefox
Justification: All kinds of good stuff week after week. Highly recommended.
Rss Link: http://pauldotcom.com/podcast/psw.xml
Name: Security Now!
Main Subject: computer security and basic technology concepts
Format: Formal
Approx. Updates Per Month: 4 to 5
Recent Subjects Covered: Parallels, Virtual PC, Application Sandboxes, Blue Pill, Vista's Virgin Stack
Justification: Despite the fact that Steve Gibson is a total tool who proves repeatedly that he knows alot less than he thinks he does, the show still touches on a number of interesting subjects that are worth tuning in for.
Rss Link: http://leoville.tv/podcasts/sn.xml
Name: Binary Revolution Radio
Main Subject: hacking, phreaking, computer security
Format: Casual
Approx. Updates Per Month: 4 to 5
Recent Subjects Covered: Toorcon, IPv6, Covert Channels, Phishing, Tunneling
Justification: Less organized but offers fresh information and interesting discussion each week
Rss Link: http://www.binrev.com/radio/podcast/
Name: PLA Radio
Main Subject: Phreaking
Format: Very Casual
Approx. Updates Per Month: 1 to 2
Recent Subjects Covered: Free Phone Calls, Beige Boxing, Deaf Relay Operators (IP Relay), Social Engineering
Justification: Covers topics related to "phone hacking". While the format is a bit strange, some of the older episodes had me laughing uncontrollably and are worth a listen.
Rss Link: http://www.phonelosers.org/rss.xml
Name: Off The Hook
Main Subject: General technology, phreaking, politics
Format: Semi-formal
Approx. Updates Per Month: 4 to 5
Justification: This show, hosted by Emmanuel Goldstein, has been running since the 80's and has become somewhat legendary in the Hacking and Phreaking communities as it's been there to document the evolution of technology. Definitely worth a listen.
Rss Link: http://www.2600.com/rss.xml
Name: SploitCast
Main Subject: new vulnerabilities, exploit code, security and technology news
Format: Casual
Approx. Updates Per Month: 1 to 4
Recent Subjects Covered: Interview with Johnny Long, ping tunneling, sensitive data on stolen laptops, Zfone, high level ISP hacks, darknets
Justification: They haven't been releasing much lately, but their episodes are usually pretty interesting. I can't find any other podcasts that discuss exploit code in great detail.
Rss Link: http://sploitcast.libsyn.com/rss
Name: Blue Box: The VoIP Security Podcast
Main Subject: VoIP Security, of course
Format: Semi-casual
Approx. Updates Per Month: 3 to 6
Recent Subjects Covered: Skype security news, interviews, VoIP fraud, recent vulnerabilities
Justification: Covers some great VoIP-related security-centered information.
Rss Link: http://feeds.feedburner.com/BlueBox
Name: TWAT Radio
Main Subject: All things technology with a slight security focus
Format: Casual
Approx. Updates Per Month: 10+
Recent Subjects Covered: Newsgroup readers, Wireless attacks for dummies, Eggdrop, Wake On Lan, Network Recon, VPNs, The GIMP, Cygwin
Justification: Covers a great deal of different technology subjects
Rss Link: http://www.twatech.org/wp-feed.php
Name: Basenet Radio
Format: Casual
Approx. Updates Per Month: 2 to 4
Justification: Underground feel, great information
Rss Link: http://www.basenetradio.net/rss2.xml
Name: LugRadio
Main Subject: Linux and Open Source
Format: Casual
Approx. Updates Per Month: 0 to 2
Recent Subjects Covered: the Portland Project, trusted computing, comparison of Linux distributions, Software Freedom Day
Justification: Possibly the most popular Linux-related podcast
Rss Link: http://www.lugradio.org/episodes.rss
Name: The Linux Link Tech Show
Main Subject: The cutting-edge in Linux-based technology
Format: Casual
Approx. Updates Per Month: 4
Recent Subjects Covered: Linux Home Automation, OpenWRT, Asterisk, Debian vs Mozilla, DRM
Justification: Lots of good Linux-related information
Rss Link: http://www.thelinuxlink.net/tllts/tllts.rss
Name: StillSecure, After all these years
Main Subject: All things related to information security with a focus on a business environment
Format: Formal
Approx. Updates Per Month: 2 to 5
Recent Subjects Covered: Interview with Steve Hanna of Juniper Networks, TCG/TNC, The IETF, 3rd party patching
Justification: This podcast includes some great interviews and information centered around enterprise security
Rss Link: http://clickcaster.com/clickcast/rss/1653
Name: Symantec Security Response Podcast
Main Subject: Security updates
Format: Formal
Approx. Updates Per Month: 2 to 4
Justification: A consistent source of security updates - great for people who are charged with defending a network for a living
Rss Link: http://www.symantec.com/content/en/us/about/rss/sr/sr.xml
Name: Network Security Blog
Main Subject: Network Security…
Format: Formal
Approx. Updates Per Month:
Rss Link: http://www.mckeay.net/secure/index.xml
Saturday, October 14, 2006
How to use your PC and Webcam as a motion-detecting and recording security camera
Web site Simplehelp has a tutorial for setting up your own motion-detecting security camera - all you need is a PC, a webcam, and a free, open source program called Dorgem.
Simplehelp's instructions are very detailed, and in the end you should have a security camera that can, for example, take pictures of intruders and upload them to a remote location via FTP (just in case the computer gets stolen). Or maybe you'll just end up with a lot of pictures of your son doing things in front of your computer that you never wanted to know about. Either way (well - not so much the second way), this is pretty cool. Works on Windows 98 and up.
Saturday, October 07, 2006
Hacking the Hacker
This "Hacker" site has Kevin Mitnick's "Art of Deception" book in pdf format. Kind of seems a little ironic...
VoIP Scanning
Interesting post on VoIP scanning...
Full story here.
What’s seems to be happening is that someone in France (from the IP address 82.234.27.188 from all the reports I’ve seen) is trying to find insecure SIP devices. They’re doing this by trying to make a call to 0033147310370, which appears to be a Fax machine or modem of some type in France. It’s a bit silly, actually, as ‘00′ isn’t a valid International code in lots of places - here in Australia, for example, the international dial prefix is ‘0011′, and in the US it’s ‘011′, so it’s always going to return a 404 here, no matter even if I do have a misconfigured device.
Friday, October 06, 2006
Friday Fun - DVD Rewinder
Time to start Christmas shopping! Get yours here.
Are you ready for HD-DVD? How about Blu-Ray? The DVD Rewinder works with any format! These new technologies can't get one up on this amazing device. Get your friends, and family out of the doldrums with the best and unique gifts on the internet. We are expanding our product line with truly unique and hard to find items.
Sunday, October 01, 2006
Non-Encrypted Hall of Shame
A list of companies who did not take prudent steps to guard their personal information.
Shopping Mall Security in the year 2017
Chris Oakley’s experimental short film, “The Catalogue” is a video scenario of what a shopping mall’s security would be like with the implementation of RFID tags used for real-time surveillance.
Saturday, September 30, 2006
Does Crime Pay? Reselling Stolen Information
From the folks at F-Secure:
Haxdoor rootkit-equipped backdoors are widely used - in the "Rechnungen" and "Räkningen" spam runs in Germany and Sweden for example.
These changing Haxdoor variants are generated with a toolkit known as "A-311 Death".

The toolkit itself is sold on the Internet by its author, known as "Corpse" or "Korpsov".
Now, people who use such backdoors quickly collect a lot of information from infected computers. Information such as passwords, credit cards, and bank logons. Some of these attackers filter the logs they collect to find juicy information and then use it themselves. Others grep the data for e-mail addresses (to sell them to spammers) and for credit card numbers and bank logins (to sell them to fraudsters).
Then again, others take the easy way out and end up selling the logs as they are, by the megabyte. Here's a screenshot from one forum:

Wednesday, September 27, 2006
Google for SQL Injection
Security expert Michael Sutton of SPI Dynamics wrote a little tool which uses the Google web search API to locate SQL injections, opening another chapter in the big book of Google hacking.
IMMUNIZING THE INTERNET, OR: HOW I LEARNED TO STOP WORRYING AND LOVE THE WORM
An anonymous note in the Harvard Law Review argues that there is a significant benefit from Internet attacks:
This Note argues that computer networks, particularly the Internet, can be thought of as having immune systems that are strengthened by certain attacks. Exploitation of security holes prompts users and vendors to close those holes, vendors to emphasize security in system development, and users to adopt improved security practices. This constant strengthening of security reduces the likelihood of a catastrophic attack -- one that would threaten national or even global security. In essence, certain cybercrime can create more benefits than costs, and cybercrime policy should take this concept into account.
Tuesday, September 26, 2006
VR Gear Makes RC Airplane the Coolest Toy Ever
This is just too cool...
A Canadian RC airplane enthusiast shows us some sweet unanticipated convergence between a model RC airplane and virtual reality gear. It works like this: The airplane is a conventional one, controlled by a wireless remote control. On the airplane is a pan-and-tilt camera, controlled also wirelessly. Here's the cool part. The video is viewable through virtual reality goggles, which have a gyroscope built in to sense the movement of the goggles. When the wearer moves his head, the camera moves. Tragically, this is not a product you can buy, but a DIY project.
www.hak5.org - USB Password Leecher
"In this segment we'll overview a few of Microsoft Window's security weaknesses and show how to build a custom USB key that will retrieve vital information from a target computer, necessary for auditing password strength. A major flaw in the way Windows stores password information is the use of the legacy LM, or LAN Manager hash. While this hash is based on DES encryption it is vulnerable to time-memory trade-off attacks due to it's poor implementation. Our custom USB key uses new U3 technology to automatically and invisibly retrieve these weak hashes within seconds of being inserted into the target computer. From here the LM hashes can be tested against a set of rainbow tables using the popular rainbowcrack software and audited for password strength. We will also cover password best practices and prevention methods for this type of attack."
Episode 2×02 Release
Saturday, September 23, 2006

Friday, September 22, 2006
Fridays are for Fun - Securing World Peace
World Peace Through Male Restroom Etiquette - A much needed, eye-opening tutorial (using The SIMS) to create a safer, more respectable world....
Sunday, September 17, 2006
WirelessDefender.net
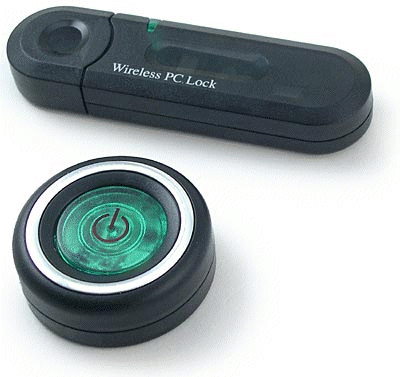 A support site for the Wireless Defender knuckleheads, with a community that is busy hacking on UsbWiSec.
http://www.wirelessdefender.net
Gone Phishing...
$163K Wow... It is hard to believe that there are that many gullible folks still around, but it is Kentucky...
Scam artists using fake e-mails purportedly from Fifth Third Bank have stolen $163,000 from the Northern Kentucky Chamber of Commerce's bank accounts. It's the highest-profile case since the Cincinnati bank - the nation's 11th-largest - became a target for "phishing" scams this summer. Phishing is the act of tricking someone into giving confidential information or tricking them into doing something they normally wouldn't. Crooks typically use banks' and other financial-services companies' IDs because of their large customer bases. According to the anti-virus company McAfee, Fifth Third made up 60.5 percent of all phishing attacks in August. Working with the FBI, the chamber has recovered $65,465 and has traced $43,541 more that is pending recovery. Chamber president Steve Stevens said in a news release that the chamber is financially stable.
Kevin Mitnick on NPR (audio)
Q&A with Kevin Mitnick (among others) on Talk of the Nation (September 14) about social engineering, pre-texting, and privacy issues in light of the recent HP scandal. His portion starts about nine minutes into the program.
Tuesday, September 12, 2006
NetCat Tips - Quiet Exploration of Ports
Let's go...
We all know about netcat, so I won't do an introduction about it. Instead I will talk about the use of netcat in the quiet exploration of ports. As Netcat can talk with a range of ports, an obvious use for it will be to use it as ports' explorer. The first impulse is to connect Netcat to a complete range of ports on the target system.
[root@peruvian nc]# ./nc target 20 - 80
This will not work. Remember that Netcat is not a port scanner. In this situation, Netcat will start at port 80 and will try to carry out TCP connections to any ports that respond. As soon as it receives an answer on a port, Netcat will wait for a standard response before continuing. This Behavior is not the one that we are looking for.
The option -z is the answer. This option will tell Netcat to send a minimum amount of data to obtain an answer from an open port. When the -z switch is used netcat will not be able to send data to the remote port and as soon as the port is open it is immediately shutdown and closed. This allows us to avoid waiting for a response before continuing.
The verbose switch (option -v) provides details on the connections that Netcat is carrying out so will be able to use this to see the results of its analysis of the ports. Without this option,… well…, it will not be able to see anything. An example follows next:
[root@peruvian nc]# ./nc -z 192.168.1.100 20-80
[root@peruvian nc]# ./nc -v -z 192.168.1.100 20-80
peruvian [192.168.1.100] 80 (www) open
peruvian [192.168.1.100] 23 (telnet) open
peruvian [192.168.1.100] 22 (ssh) open
peruvian [192.168.1.100] 21 (ftp) open
[root@peruvian nc]#
When using the -v switch, we can see the status of the ports of some of the usual services running on the remote machine. What will our scan look like in the logs of the target system?
July 16 16:15:12 peruvian sshd[21690] : Did not receive ident string from 192.168.1.105
July 16 16:15:12 peruvian telnetd[21689] : ttloop: read: Broken pipe
July 16 16:15:12 peruvian ftpd[21691] : FTP session closed
We see that traces of our activity have been left on the target system. The system tracks the moment we scanned and the list of consecutive processes (21689 to 21691) we explored. If we had scanned a greater range of ports it would have left a really huge track in the logs of the target system. Also certain services, for example sshd, are so bad-mannered that they will save the IP address of the scanner.
Even if we scan a port on which nothing is running (and therefore the connection will not be logged), most networks count on intrusión detection systems that will immediately indicate this type of malicious behavior and they will call the attention of the administrator. Some Firewall applications will also block an IP address automatically if they receive too many connections on in a brief period of time.
Netcat allows the execution of a more sophisticated way to avoid this :D. We will be able to use option -i and to form a test interval. It will take a little more time to obtain the data, but the exploration with this allows more events to happen between each connection to help keep us off of the radar.
If we use the option -r so that Netcat explores of random form these ports, this process will look even less like an exploration of ports:
./nc -v -z -r -i 42 192.168.1.100 20-80
The previous instruction tells Netcat to choose a random range of ports between positions 20 and 80 in the 192.168.1.100 address and to try to connect to each one of them every 42 seconds. This method should bypass any automated defensive system, but the evidence of the exploration will continue to exist in the registries of the target system; they will only be more disordered.
You can also use netcat to carry out a quiet exploration of ports using UDP. All you need to do is add the -u option to instruct netcat to explore UDP instead of TCP ports.
*Note1:
Scanning with the UDP protocal has a problem. Netcat depends on the reception of an Internet Control Mensajes Protocol (ICMP) to determine if a UDP port is open or closed. If the ICMP is being blocked by a Firewall or a filter, Netcat will falsely report that these UDP ports are open.
Netcat is not a very sophisticated port scanner. One of its main features is that it is a very good general tool and does not emphasize any specialty. For this reason it is better to use a specifically developed port analyzer.
*Note2:
If you're getting errors when trying to port scan, try to limit netcat to a specific IP address and a specific port by using the -s and -p switches. Choose a port below 1024 or a port that isn't used by any service.
More questions:
----------------------
root3d
system666x@gmail.com
Perú [16/07/2006]
16:44
----------------------
Personal Security - Wear A Bike Helmet, Get Hit!
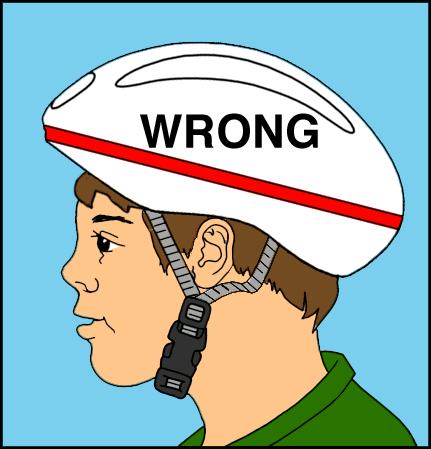 Cyclists who wear helmets are more likely to be knocked down by passing vehicles, research suggests.
A study found that drivers tended to pass closer when overtaking cyclists wearing helmets than those who were bareheaded, by 8.5cm on average.
Dr Ian Walker, a lecturer at Bath University, used a bike fitted with a computer and an ultrasonic distance sensor to analyse 2,500 overtakings in Salisbury and Bristol. He was struck twice during the experiment, by a bus and a lorry, while wearing a helmet.
Saturday, September 09, 2006
Security at Disney?
 So... How did they get the thing through the "security" checkpoint at the front gate?
A mannequin depicting a prisoner described as a Guantanamo Bay victim, was reportedly snuck into one of the dioramas alongside of Disneyland's Big Thunder Mountain last week.
Monday, September 04, 2006

Saturday, September 02, 2006
The "Janus Project"
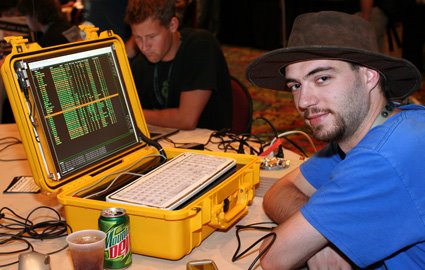 The "Janus Project" is the brainchild of Kyle Williams of the Janus Wireless Security Research Group in Portland, Oregon.
Mounted inside an epoxy and silicone-sealed watertight case lives a 1.5GHz C7 powered EPIA EN 15000G motherboard, 2 x four-port PCI to mini-PCI adapters, 8 x 802.11a/b/g mini-PCI WLAN Modules, 2 x 1W 2.4Ghz WLAN amplifiers, a keyboard and a 17in LCD screen. The system can scan up to 300 wireless networks simultaneously, storing and AES encrypting in real time all the data onto its 20GB hard drive.
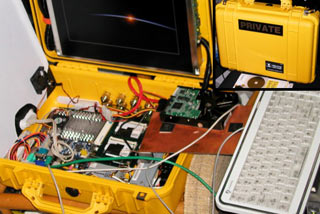
By focusing all 8 WLAN cards onto an access point and using a combination of common Linux tools, the Janus Project can crack a WEP key in under 5 minutes. WPA and WPA2 encryption aren't far behind - Kyle and his friend Martin Peck are optimising the software to use the Padlock hardware acceleration of the C7 chip to crack those too.
If Kyle gets captured in enemy territory and tortured, an "Instant Off" switch will render the captured data useless until a password is entered and a USB stick containing a 2000-bit passkey is inserted. Presumably during the torturing process.
Friday, September 01, 2006
Friday Fun - Burning Man 2006 TV
 Burning Man 2006 is now in full swing and Current TV has setup an online television station, TV Free Burning Man.
They have been shooting video, doing interviews and uploading a daily show from Black Rock City. They will be doing a live broadcast the burn on Saturday night (September 2nd) starting at 9 PM PST/12 AM EST.
Thursday, August 31, 2006
Turning IE into a private Adult Content Browser
Privacy View Software, LLC, announces the release of Privacy View 2.10, a new version of the company’s privacy software for adults. Privacy View is part privacy software and part content management software aimed at people who surf for adult content. The new version of the software was release August 31, 2006.
PI announces the 2006 Stupid Security Competition
Privacy International is calling for nominations to name and shame the worst offenders. The competition closes on October 31st 2006. The award categories are:
- Most Egregiously Stupid Award
- Most Inexplicably Stupid Award
- Most Annoyingly Stupid Award
- Most Flagrantly Intrusive Award
- Most Stupidly Counter Productive Award
The competition will be judged by an international panel of well-known security experts, public policy specialists, privacy advocates and journalists.
The competition is open to anyone from any country. Nominations can be sent to stupidsecurity@privacy.org.
Details of previous award winners can be found below, or at http://www.privacyinternational.org/ssa2003winners.
WIFI Camera Prototype
 Nice use for the cans from a favorite snack...
The WiFi Camera Obscura uses a directional WiFi antenna as an aperture for taking "pictures" the radio energy from WiFi use in a room, and paints those pictures as a movie on a nearby wall. The pictures are lovely oil-slicks of revealed radiation.
Wednesday, August 23, 2006
Blackjacking - 0wning the Enterprise via the Blackberry
Presented at Defcon 14 - Las Vegas, NV 2006 by Jesse D'Aguanno
Abstract:
Abstract:
Research in Motion's Blackberry technology has quickly become the defacto standard for executives and technical personnel alike to maintain unteathered remote access to critical data. Often regarded as inherently secure, most administrators deploy this solution without a full understanding of the technology or risks involved.
This presentation will demonstrate how an attacker could utilize many typical corporate blackberry deployments to directly attack machines on the internal network—behind your perimiter defenses! The tools and source code presented will be available for attendees. Techniques for reducing the risks associated with this technology will also be presented.
This presentation will demonstrate how an attacker could utilize many typical corporate blackberry deployments to directly attack machines on the internal network—behind your perimiter defenses! The tools and source code presented will be available for attendees. Techniques for reducing the risks associated with this technology will also be presented.
Materials:
| Presentation Slides | Blackberry Attack Toolkit (Including BBProxy) |
Tuesday, August 22, 2006
Privacy Debacle Hall of Fame
Wired News lists what it considers to be the 10 greatest privacy disasters:
10. ChoicePoint data spill
9. VA laptop theft
8. CardSystems hacked
7. Discovery of data on used hard drives for sale
6. Philip Agee's revenge
5. Amy Boyer's murder
4. Testing CAPPS II
3. COINTELPRO
2. AT&T lets the NSA listen to all phone calls
1. The creation of the Social Security Number
10. ChoicePoint data spill
9. VA laptop theft
8. CardSystems hacked
7. Discovery of data on used hard drives for sale
6. Philip Agee's revenge
5. Amy Boyer's murder
4. Testing CAPPS II
3. COINTELPRO
2. AT&T lets the NSA listen to all phone calls
1. The creation of the Social Security Number
Friday, August 18, 2006
Blackhat 06 Presentations
Didn't make it to BlackHat in Las Vegas this year? Well you can at least take a gander at the presentations online. They're available here as PDF's.
Cool speed test site
Speedtest.net is a general use broadband connection testing site with many geographically dispersed servers to test against. Plus it looks very cool...
Wireless networking source - .\\etrix Communication LLC
 Interesting source for wireless networking software, parts, supplies and info.
Fridays are for fun! Secret Agent Earphones
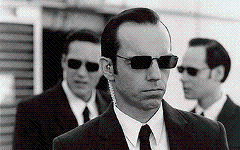 Easy way to make FBI-escque earphones. This is very useful if you ever want to listen to music but also have one ear free (for instance while biking in the city)
Sunday, August 06, 2006
Mystery hole opens in Cisco firewall
Some vendors like CheckPoint do one thing and do it extremely well... Others like Cisco do lots of things with mediocrity...
A security researcher has demonstrated how an unpatched vulnerability in Cisco?s PIX firewall appliances could allow outside attackers to gain access to corporate networks. On the final slide of his presentation at the Black Hat show on VoIP security, Hendrik Scholz, a developer with Freenet Cityline disclosed a technique for bypassing the firewalls, according to an audio recording of the talk obtained by IDG News. "You can open up whatever port you want... and access internal servers from the outside," he said "It's really easy to do and we're talking to Cisco about how to get it fixed." By now Black Hat is old hat for Cisco. Last year conference organisers were sued by the networking giant and had to literally rip a presentation by researcher Michael Lynn out of last year's conference materials because it disclosed flaws in its IOS software.
Phone numbers stations mystery revealed at DEFCON
For three months, mysterious telephone numbers have been appearing on the Craigslist classified ad site which, when called, play recordings which sound much like shortwave numbers stations used by certain governments to communicate with intelligence agents in the field who are unreachable by other means. Now the secret behind these phone numbers stations has been revealed.
Read the whole story here.
Read the whole story here.
Friday, July 28, 2006
Hak5

Hak.5 is a video podcast for the hacker, modder and do-it-yourselfer. Hosted by Darren Kitchen and Wess Tobler on the 5th of each month, the show is a hybrid of technology and geek humor.
TOOOL, The Open Organisation of Lockpickers
 Weekend fun... Ck the blackbag blog for info from Hope # 6 and a look at the very nice Hope number six pickset...
Dilbert - funny in a scary way...
 Tuesday's Dilbert (quoted below, copyright Scott Adams, Inc) funny in a scary way...
Dilbert: Is it more important to follow our documented process or to meet the deadline? I only ask because our deadline is arbitrary and our documented process was pulled out of someone's lower torso.
PHB: Where's your artificial sense of urgency?
Dilbert: Teamwork killed it.
Cool and Illegal Wireless Hotspot Hacks
Nice article / tutorial by wireless guru, Dan Hoffman of 'Live Hacking Video' fame. As he often does, here he takes you step-by-step through some sweet wireless hacks and then shows you how to protect yourself from them..
Wednesday, July 19, 2006
Shark Analyzer
At least now there shouldn't be an argument on how to pronounce the name...
The Ethereal network protocol analyzer has changed its name to Wireshark and ver. 0.99.2 has been released. Several security-related vulnerabilities have been fixed and several new features have been added.
For a complete list of changes, please refer to the 0.99.2 release notes. Official releases are available right now from the download page.
Tuesday, July 18, 2006
Phish Spoofs 2-Factor Authentication
 The first ever case of using a man-in-the-middle attack against an online bank was reported by the Post's Brian Krebs on Tuesday.
The security industry has long predicted this type of man-in-the-middle attack; it was only a matter of time. The attack targeted Citibank's Citibusiness service and was designed to spoof the token key hardware device used by the bank's customers. The phishing site checked the logon credentials with the real site before rendering the results to the phishing victim. Enter an invalid password, and you got an invalid logon page. A man-in-the-middle attack checks everything done at the phishing site against the original, so everything should look and feel more genuine.
Exactly the same kind of attacks can be used to target other types of two-factor authentication, including one-time password sheets.
Saturday, July 15, 2006
Stevens' net neutrality expertise
Eighty-two year old Sen. Ted Stevens' complete inability to comprehend the internet would be kind of cute, were it not for the fact that the following soundbites were taken from his 11-minute speech regarding a bill that would have increased network neutrality mandates.
In that light, this quote is sort of terrifying: "The internet is not something that you just dump something on. It's not a big truck. It's, it's a series of tubes.
In that light, this quote is sort of terrifying: "The internet is not something that you just dump something on. It's not a big truck. It's, it's a series of tubes.
Friday, July 14, 2006
VulnerabilityAssessment.co.uk
An information portal for Vulnerability Analysts and Penetration Testers. The Penetration test Mindmap is a treat...